One retainer replaces a security leader's salary, a consultant and a software licence, and one management system covers both standards.
Practitioner-led, technology-enabled · ISO/IEC 42001 · ISO/IEC 27001
When the next deal asks how your AI is governed, be ready.
Muster42 gets growth companies certified to ISO/IEC 42001, the AI management standard, and keeps them certified. We do the work. You make the calls.
- An experienced lead runs it. A certified practitioner builds your AI management system with your team, on an ISO/IEC 27001 security foundation.
- MusterGRC keeps it current. Our own tooling holds your policies, registers and evidence, schedules the recurring checks, and links every finding to the document it rests on.
- Someone else checks it. An independent assurance partner verifies the work before the accredited certification body audits it.
ISO/IEC 42001AI management, our focus
ISO/IEC 27001The security foundation
MusterGRCSelf-hosted GRC tooling
AssuranceIndependent verification
Practitioners · Tooling · Proof
ISO/IEC 42001 first, on a foundation that already holds.
ISO/IEC 42001 is the reason we exist and the 42 in our name. It shares its structure with ISO/IEC 27001, so we build both as one management system and you avoid the duplication, the second set of policies and the second bill. Experienced practitioners lead the programme with MusterGRC, our continuous assurance tooling. We carry the GRC workload and you retain the decisions.
Our focus
ISO/IEC 42001
AI policy, roles, impact assessment, lifecycle controls and third-party AI governance.The security foundation
ISO/IEC 27001
93 controls across four themes, with supplier and access control built in from the start.Why Muster42
AI is entering the business faster than the controls around it, and the security foundations don't exist.
01
The AI you inherit
Supplier tools nobody has assessed, and SaaS your staff switched on themselves.
02
The AI you build
Models and automations in production without lifecycle controls behind them.
03
The questions you're now being asked
Enterprise security reviews, insurance questionnaires and regulator enquiries, usually attached to the next deal.
What changes with Muster42
Lower cost. Higher quality. Always current.
Every finding cites the document it rests on, gaps are never assumed closed, and the work is verified by a third party.
Monitoring and recurring checks run all year, so each surveillance audit finds a system that is already current. Illustrative.
What certification wins you
- Security questionnaires answered with a certificate
- Eligibility for tenders that require ISO/IEC 42001 or ISO/IEC 27001
- Evidence for investors, insurers and boards that AI is governed
 The tooling behind Muster42
The technology behind the service.
MusterGRC is the tooling Muster42 practitioners use to run your programme. It runs on AI models we host ourselves, so your documents never go to a public AI service. It keeps the programme continuous, every change revised and every recurring control monitored, so certification holds between audits instead of being reassembled for them. Every judgement points back to your own documents.
SovereignAssessment runs on AI models we host ourselves, not a public AI service.
ContinuousEvidence, registers and findings stay current all year, not just at audit time.
RevisionApprovals are tied to the exact text. Change one line and only what it affects is flagged for re-assessment.
MonitoringRecurring controls are scheduled, owned and followed up, so nothing lapses before the next audit.
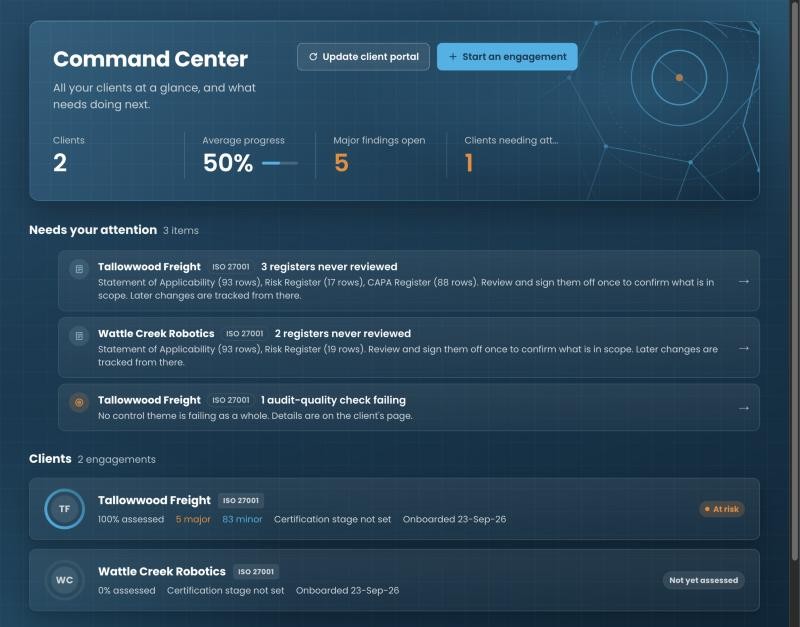
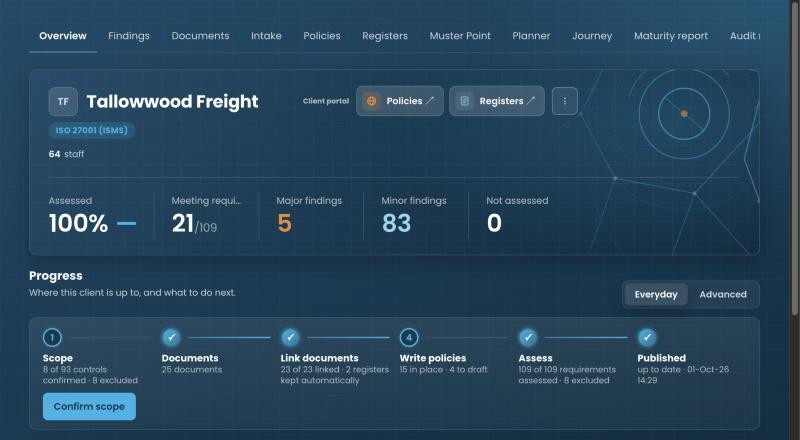
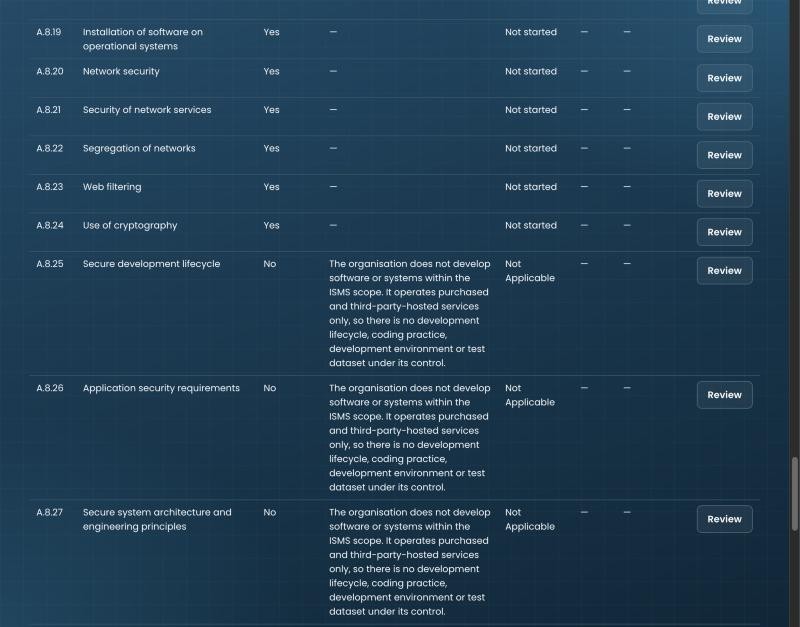
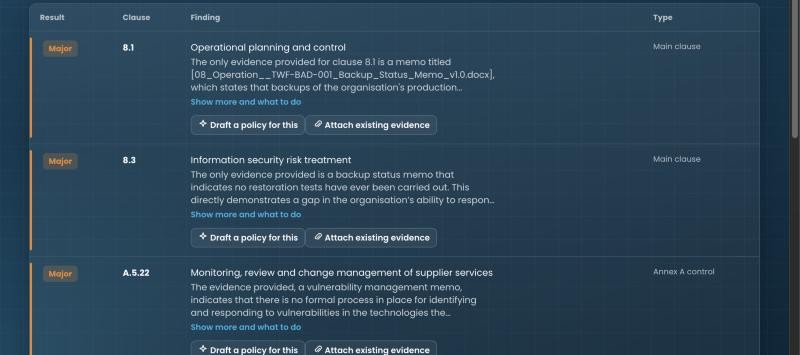
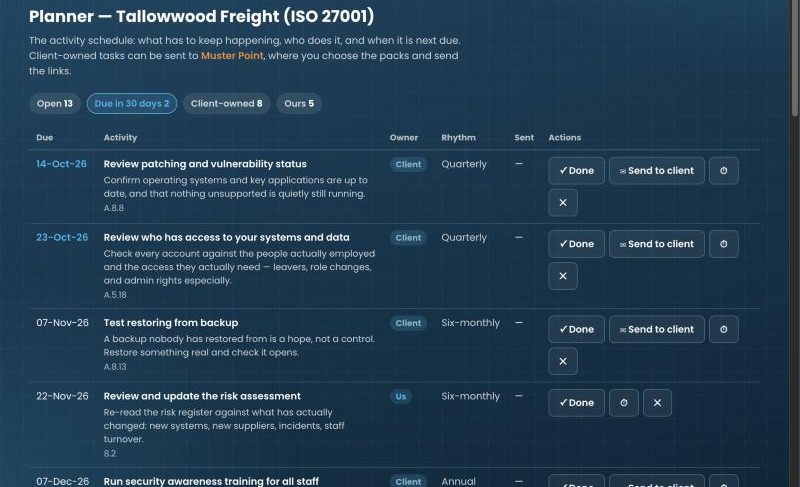
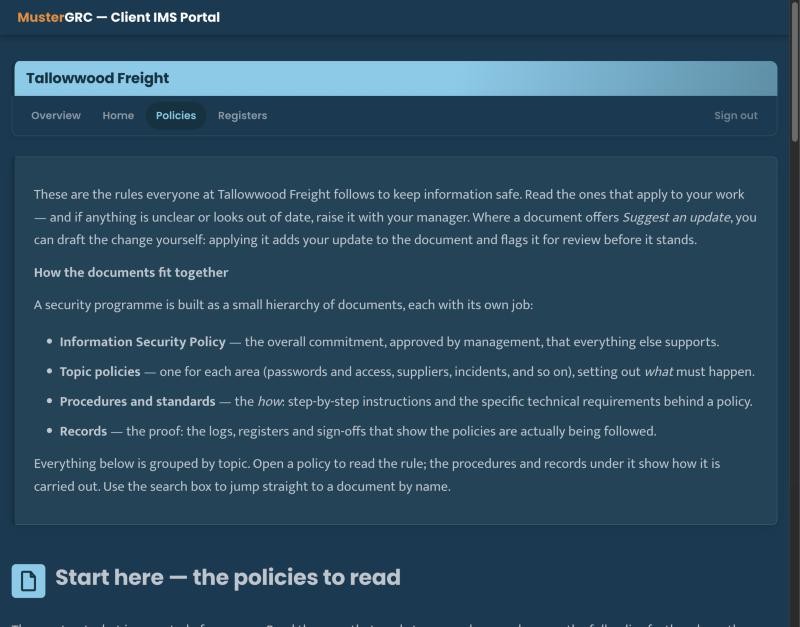
Screens from a demonstration client.
See how MusterGRC works →
A Muster42 practitioner walks you through it on a demonstration client.
What we build
What you hold at the end, and keep using.
A management system is how your company runs security and AI governance, written down and proven. Not a binder on a shelf, but a working set of documents, registers and records your team, your board and your auditor can interrogate. It has four layers:
- PolicyWhat leadership commits to
- Topic policiesWhat must happen
- ProceduresHow it is done
- RecordsThe proof it is followed
Kept alive by a yearly cycleRisk assessment → Internal audit → Management review → Improvement
 The collateral you receive
Governance documents
- Information Security Policy and AI Policy, approved by your leadership
- Topic policies: access, suppliers, incidents, acceptable use of AI
- Procedures where the policies need a how
Registers
- Statement of Applicability, with a reason for every exclusion
- Risk register covering security and AI risk
- Corrective action register, tracked to closure
Proof and assurance
- Evidence mapped to every control, cited to the document
- Internal audit report, issued and signed
- Independent verification before the certification audit
Reporting and running it
- Maturity report written for your board
- A monthly progress report
- The year's plan of recurring checks, with owners
For your staff
- A portal in your branding: published policies, registers and a plain-English guide
Independent assurance · Vero AI
A verdict that isn't ours.
The people who build your system shouldn't be the ones who mark it. Vero AI is AI audit automation built for the audit profession: AI agents with auditor review evaluate the evidence, score the controls and return cited, audit-ready findings.
Vero AI
One platform for any evidence. Any framework. Any control.
Independent assurance partner to Muster42
Separation of dutiesThe party that builds your system is not the party that evaluates it.
Cited findingsEvery finding comes back with the evidence it rests on, ready for your auditor to follow.
Certified lead auditorsVero AI is built by auditors who hold credentials in the frameworks they evaluate against.
Run as you changeEvaluation repeats as your system evolves, not once before the audit.
More about Vero AI at vero-ai.com
People lead. Technology supports.
Run by certified lead auditors.
The experienced practitioner already sitting at your table, with the credentials to back the judgement.
ISO/IEC 27001Lead Auditor
ISO/IEC 42001Lead Auditor
CISMCertified
AICDBoard perspective
For CEOs and CFOs
Certification that supports growth and stays in place.
CEO · The deal that stalls
Somewhere in your pipeline is a contract that stalls at the security questionnaire.
We get you certified, keep you certified, and you don't carry the GRC workload.CFO · Cost and risk
One retainer instead of a CISO salary, a consultant and a software licence.
A fixed monthly cost, with a programme designed to keep certification current through the next audit and the next deal.
How we work
Alongside your team, from first scope to certificate.
Ready to pass muster?
Tell us where you are and what's driving it. We'll show you the quickest route to certification, and how MusterGRC keeps you there.
Book a conversation
A practitioner replies, usually within one working day.